Making it easier to run a trusted business
Whether it’s GDPR compliance or governing across multiple frameworks - we’ve got you covered.
Book a demo

Compliance. Covered.
Learn more about all that Cerivo has to offer.
Start where you are. Scale where you need to go.
Cerivo grows with the changing needs of your business and regulatory obligations - with a solution for what you need today, and where you'll be tomorrow.
Comply

GDPR & Data Protection.
From scattered to structured - without starting from scratch. Manage your processing activities, data subject requests, and privacy documentation - all in one place.
Control

ISO 27001 & Information Security.
From multi-framework chaos to one workflow with named owners.Structure your ISMS and stay audit-ready, always.
Govern

Enterprise Governance & Risk Management
From compliance as a risk to compliance as a proofpoint. Full governance,risk, compliance, and legal intelligence - built for organisations that need to demonstrate control to regulators, boards, and auditors. All frameworks. One source of truth.
Why Cerivo
More than a platform. Everything you need to stay compliant.Most organisations don't struggle with knowing what to do - they struggle with doing it consistently, across the entire organization.Cerivo fixes that.
01
More than a Platform
Replace silos with structure.
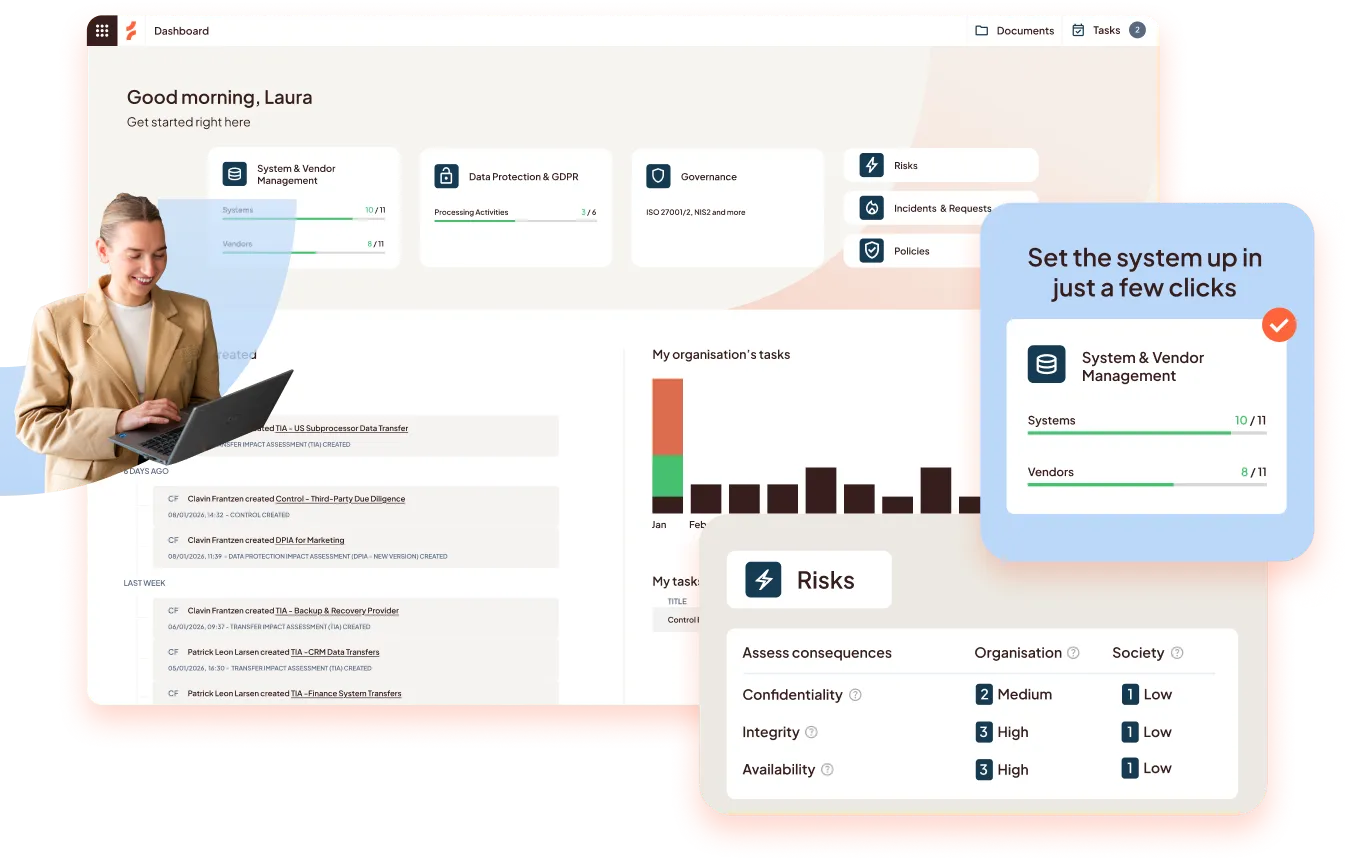
Traditional GRC platforms stop at software - not Cerivo. With an integrated platform, real human legal expertise, and a community of peers,Cerivo is a complete compliance solution, not just a tool - with everything you need to gain clarity, act with confidence, and stay in control of your compliance.
02
Legal Expertise
Software flags it. We fix it.
Cerivo comes with a team of in-house Nordic lawyers who can provide ongoing advice, support on major compliance projects, or stepping in to cover your team while someone is on leave. Real human legal expertise, on demand, that flexes with your business instead of adding headcount.
03
Peer Network Access
Join a community of people who understand your challenges.
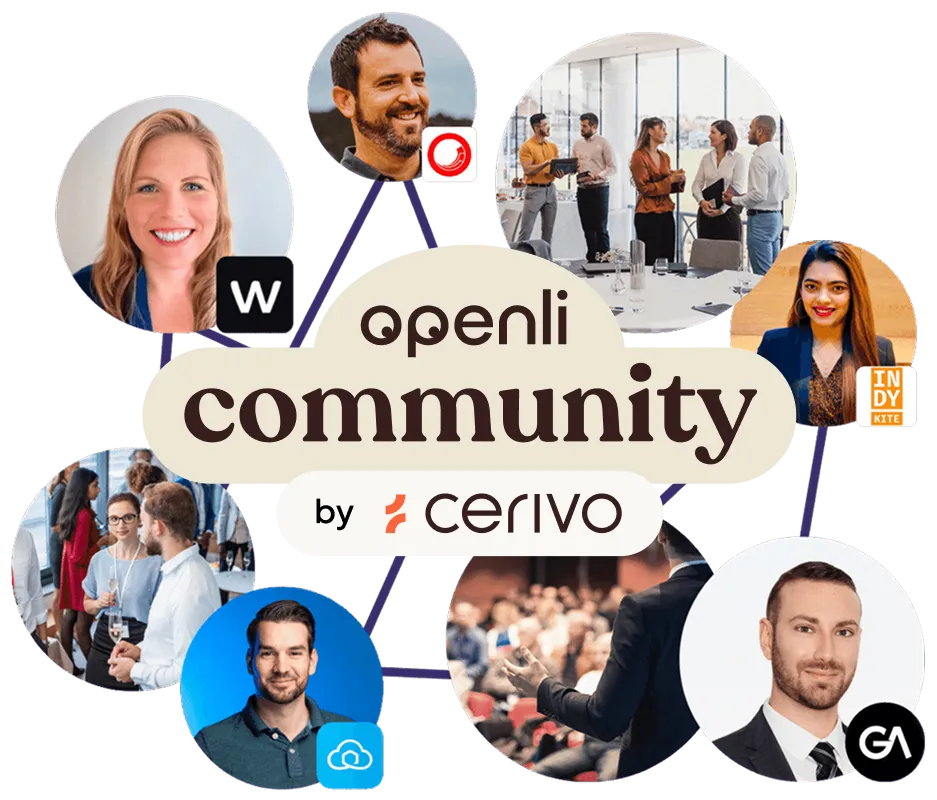
The Openli Community by Cerivo brings together 2,800+ in-house legal, privacy, and compliance professionals who share experiences, practical knowledge, and hard-won lessons through in-person events, peer conversations, expert sessions, webinars, a private Slack channel, guides, templates, and more.
Free to join. Built for people who want to learn, connect, grow, and share.
Customers
Nordic organisations that trust their compliance to Cerivo.
"One of the reasons we achieved our ISO 27001 certification was our ability to document our controls in Cerivo. Auditors could simply open a control, review the documentation, and move on."
Thorsten Kranz, Global Director Business Ethics and Compliance at Blue Water Shipping
"Cerivo has helped us successfully launch and complete compliance projects here at 3F. We enjoy a strong partnership, and we have found them to be pragmatic, highly professional, and consistently supportive, while also demonstrating a deep understanding of 3F as an organization."
Kenneth Engstrøm, Centre Manager at 3F
Nordic by design. Nordic by nature.
While traditional GRC platforms adapt to Nordic regulations, Cerivo was built inside it.
EU-hosted
No data leaves the EU.
Schrems II compliant
Transfer rules built in.
Built for GDPR, NIS2, DORA, AI Act & more
European frameworks, natively.
Team of in-house lawyers
Real legal expertise, on demand.