Managed Services
Keep compliance moving, without carrying it all in-house
Compliance isn't finished when the project ends.
Cerivo Managed Services handles the ongoing work with you – from external DPO services to policies, risks and requests across GDPR, NIS2, the AI Act and DORA.
Servicesday to day

Ongoing compliance, handled
Most organisations don't need another report telling them what needs to happen.
They need someone to help make sure it happens.
Our team combines legal expertise with experience from regulators, consultancies, financial services and in-house compliance – and works directly with you to keep routines, documentation and follow-up on track.
What we can manage with you

GDPR
Ongoing GDPR operations, including:
- External DPO services and ongoing advice
- Data processor oversight
- Handling data subject requests
- Maintaining policies and procedures
- Keeping your records of processing (Article 30) up to date

NIS2
Keep your information security work moving after implementation:
- Maintaining risk management and preparedness
- Ongoing reporting and audit readiness
- Supplier management follow-up
- Maintaining policies and procedures

AI Act
Keep AI governance and documentation up to date as your use of AI develops:
- Classification and follow-up of new AI systems
- Ongoing compliance for high-risk AI
- Documentation and governance
- Awareness activities

DORA
For organisations under DORA, we help maintain:
- Ongoing ICT risk monitoring
- Third-party registers and contracts
- Preparedness plans
- Policies and procedures
Work with people who know your business
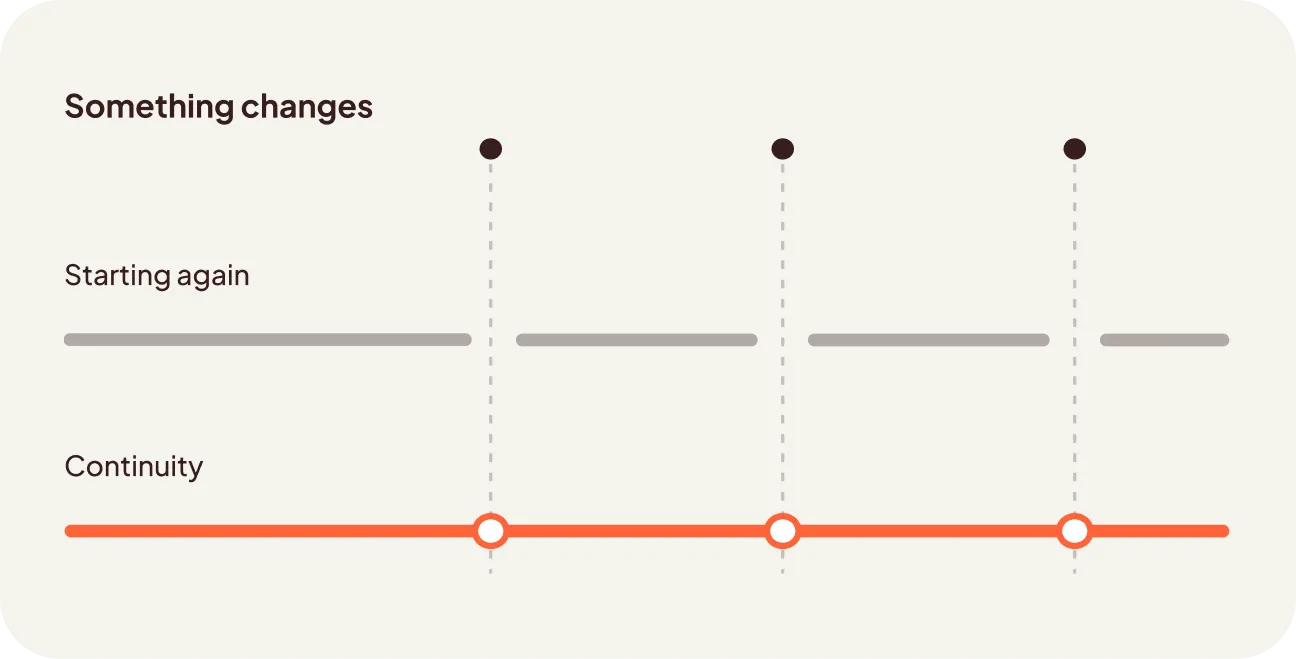
Managed Services becomes part of how your organisation works. Instead of starting over every time something changes, you work with specialists who know your setup, priorities and compliance environment.
That gives you continuity – and frees your internal team for the work that needs them most.
Clear oversight through the Cerivo Platform
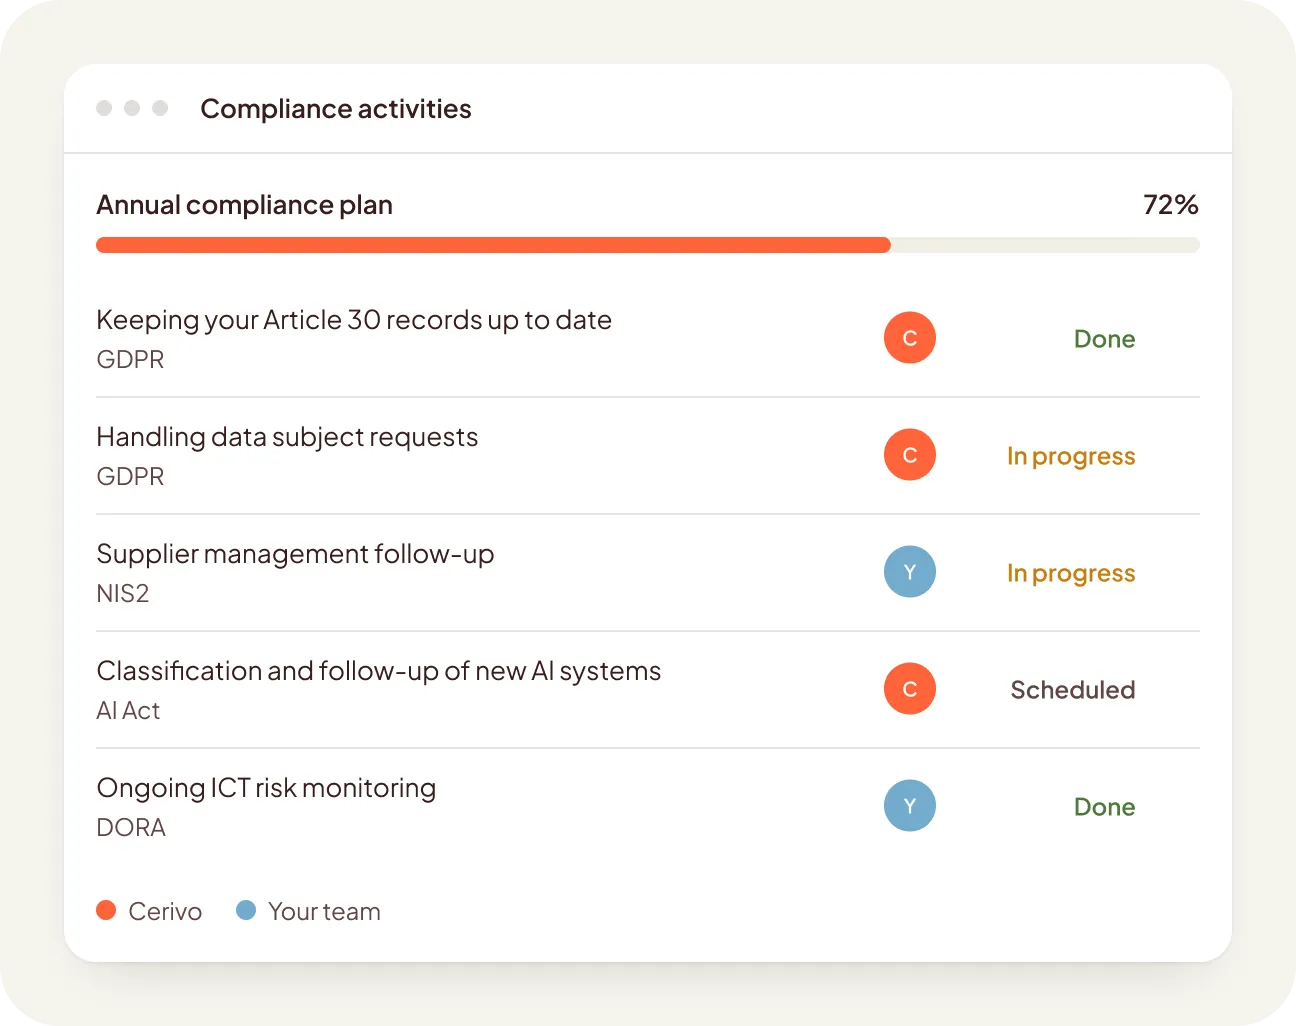
We help run the work. You keep the overview.
Documentation lives in the Cerivo Platform, so you always have access and a clear view of your compliance activities.
And if you bring more of the work in-house, it's already structured.
Your Managed Services team
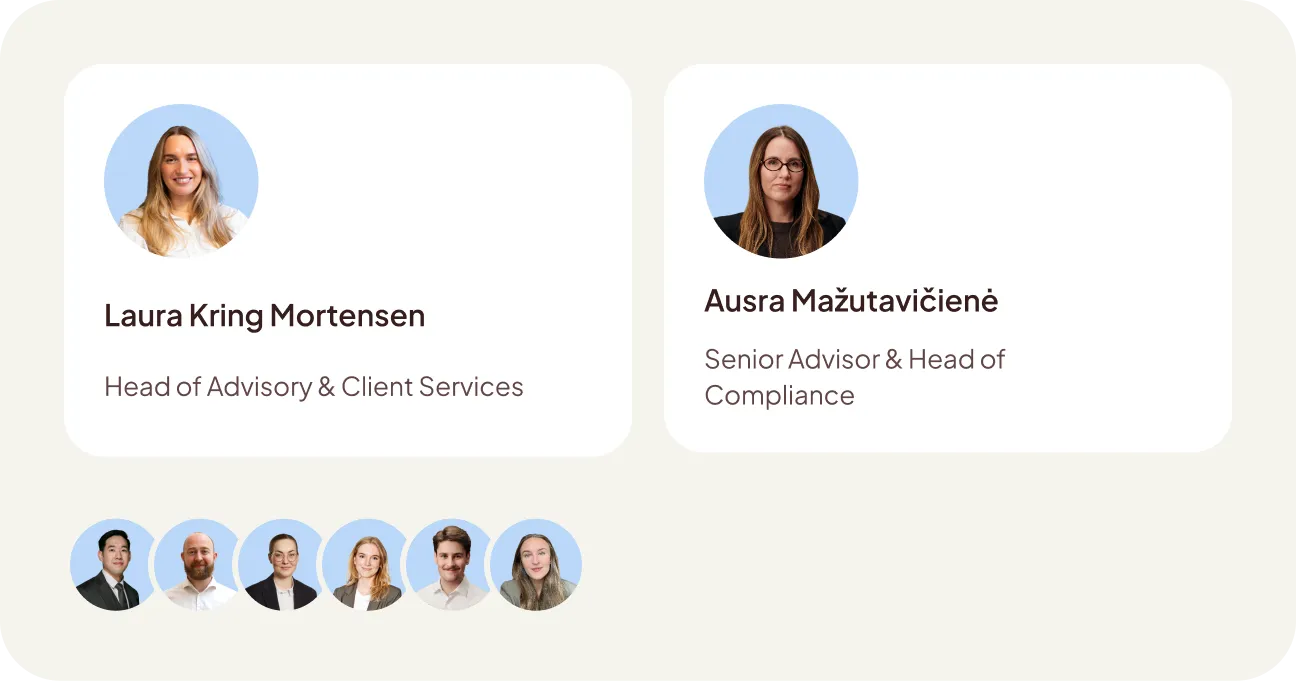
Managed Services is led by Laura Kring Mortensen, Head of Advisory & Client Services, and Ausra Mažutavičienė, Senior Advisor & Head of Compliance.
The wider team – Tony Dai, Simon Ropstad Nielsen, Alberte Kruse, Clara Rohrberg Jessen, Lester Adamsen and Sine Løvhøj Pedersen – covers GDPR, DORA, NIS2 and day-to-day compliance operations.
Meet the team