Turning Cybersäkerhetslagen compliance into lasting cyber resilience
Date:
Recorded on:
September 24, 2026
|
10:00-11:00 (CET)
As Swedish organisations prepare to implement Cybersäkerhetslagen, many are also strengthening their Governance, Risk and Compliance (GRC) programmes.
But compliance alone isn’t enough. While frameworks, policies and technical controls are essential, most cyber incidents still involve human behaviour, making employees a critical part of any organisation’s cyber resilience strategy.
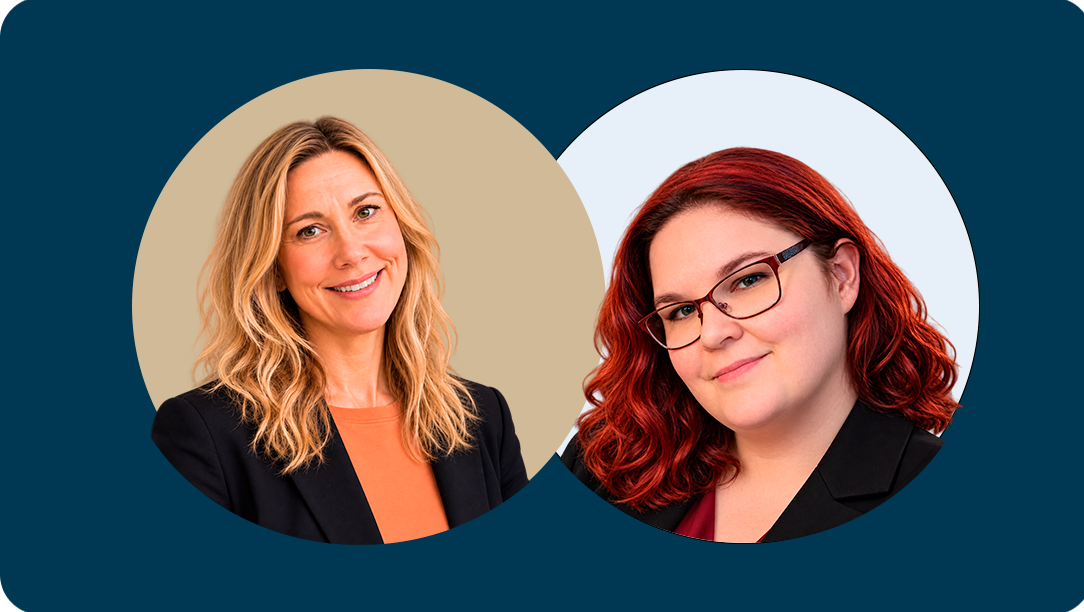
In this webinar, Linda Simonsen, Senior Advisor – GRC Solutions at Cerivo, and Sabrina Sabina Johansson, Cyber Security Expert, will explore how organisations can turn compliance with Cybersäkerhetslagen into an opportunity to build lasting cyber resilience.
You’ll learn how to avoid fragmented efforts, governance gaps and duplicated work by integrating the human element into your resilience strategy.
Discover how a strong security culture strengthens governance, improves risk management and helps organisations meet regulatory requirements while becoming more resilient to evolving cyber threats.
In this webinar, we’ll cover:
- What Cybersäkerhetslagen means for Swedish organisations and why it’s more than a compliance exercise
- How to prepare without creating fragmented efforts, governance gaps or duplicated work
- How cybercriminals exploit human behaviour and why this needs to be part of your risk management strategy
- How publicly available information, including LinkedIn, is used in social engineering and what this means for organisational resilience
- Practical steps to align people, processes and technology to build lasting cyber resilience
Fill in the form to receive the webinar recording and presentation after the event.

Complete the form below to watch on-demand
Complete the form below to register for the webinar