
How to stop AI risks from becoming cybersecurity incidents
Date:
Recorded on:
November 24, 2026
|
10:00-11:00 (CET)
If an AI-related security incident happened tomorrow, would you know who was responsible?
For many organisations, the honest answer is no. AI has moved into everyday work faster than governance has kept up. Employees use AI tools to save time, suppliers build AI into the systems you depend on, and attackers use it to make phishing and fraud harder to spot.
Turn AI requirements into clear responsibilities
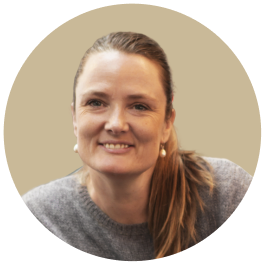
In this webinar, Stine Mangor Tornmark, VP of Legal, Compliance and Advisory Services at Cerivo, shows you how to identify and manage AI-related security risks, set clear responsibilities and turn regulatory requirements into cybersecurity measures that work in practice.
During the webinar, we will explore:
- What the AI Act, NIS2 and GDPR require of your AI use
- How to set up AI governance with clear roles andoversight
- How to manage risks when you buy, implement and use AI
- How to spot gaps between your policies and actual practice
- How to prioritise actions and track progress
Fill out the form tojoin the webinar and receive the recording after wards.

Complete the form below to watch on-demand
Complete the form below to register for the webinar